
Information Security & Risk Management
We help organizations manage information security risks, strengthen governance and implement effective controls aligned with ISO 27001, NIS2 and DORA.

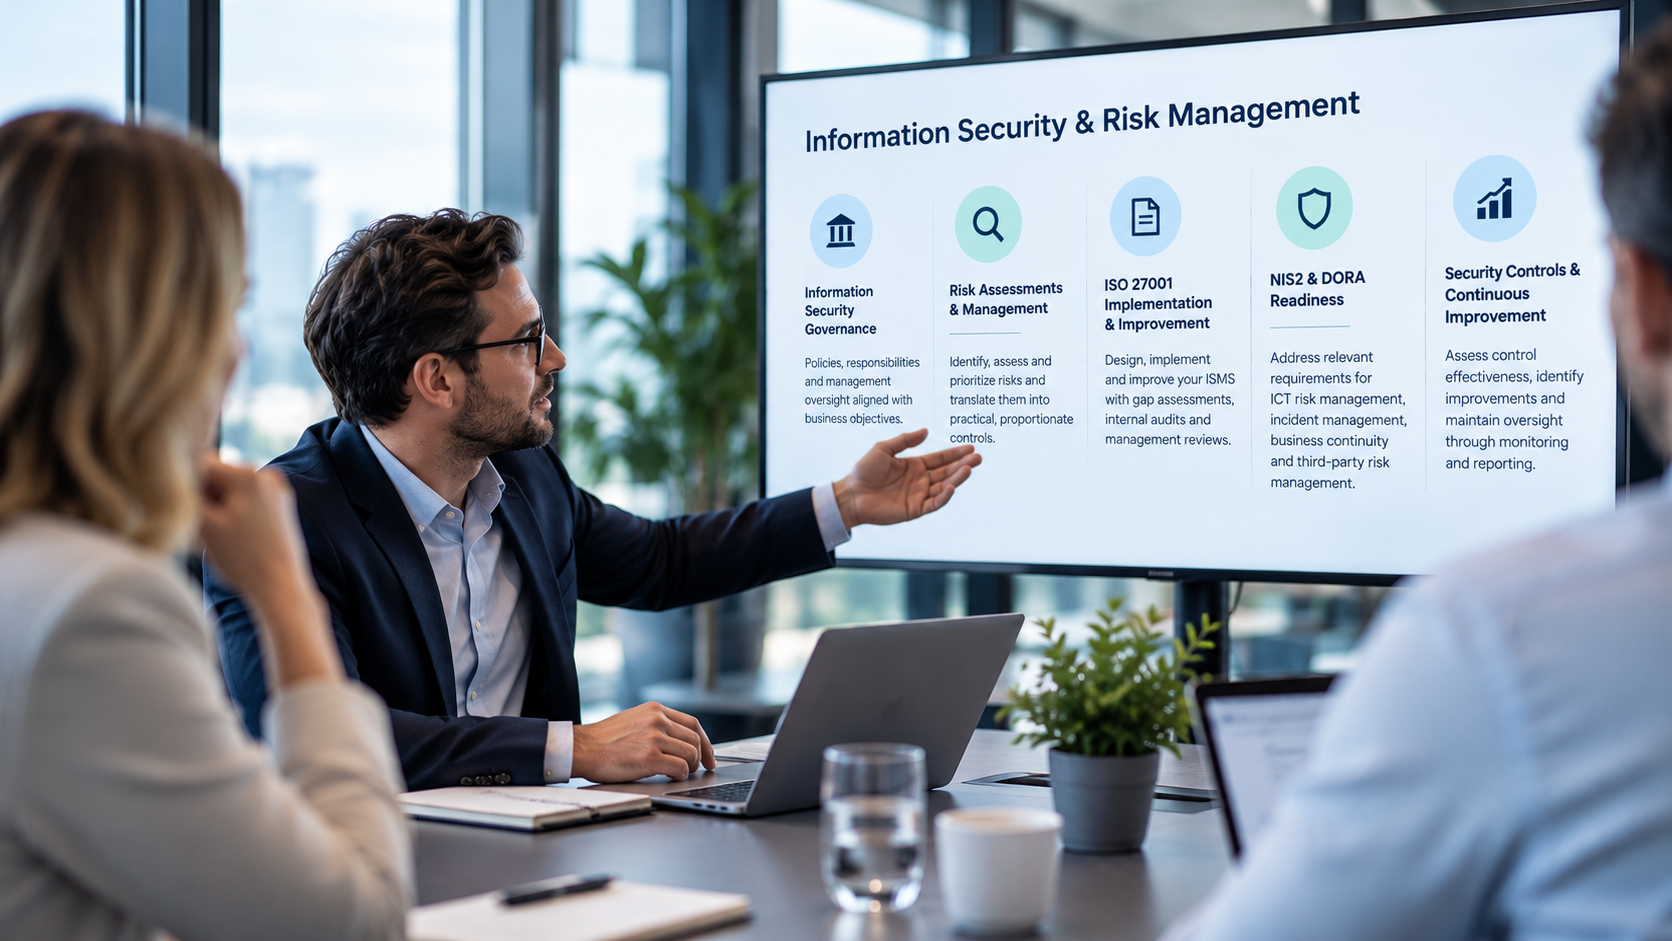
What We Offer
Information Security Governance
We help organizations establish and improve information security governance, including policies, responsibilities, decision-making structures and management oversight. Our approach aligns security objectives with business priorities and regulatory requirements.
Risk Assessments & Management
We identify, assess and prioritize information security risks and translate them into practical, proportionate controls. This includes risk treatment planning, control effectiveness assessments and ongoing risk monitoring.
ISO 27001 Implementation & Improvement
We support organizations in designing, implementing and improving their Information Security Management System (ISMS) in line with ISO 27001. From gap assessments and risk management to internal audits and management reviews, we help build a sustainable approach to information security.
NIS2 & DORA Readiness
We help organizations understand and address relevant requirements under NIS2 and DORA, including ICT risk management, incident management, business continuity, third-party risk management and governance.
Security Controls & Continuous Improvement
We assess the design and effectiveness of security controls, identify opportunities for improvement and help organizations maintain oversight through structured monitoring, reporting and continuous improvement.
Information Security & Risk Management
Information Security & Risk Management
Effective information security starts with understanding your organization's risks. At Contrisity, we help organizations establish practical governance structures, implement proportionate security controls and build resilience against evolving threats and regulatory requirements.
Our approach combines information security expertise with a strong understanding of governance, risk management and internal controls. We focus on solutions that work in practice, rather than compliance documentation alone.
A Risk-Based Approach to Information Security
Every organization faces different risks depending on its activities, technology, suppliers and regulatory environment.
We help identify and assess these risks, determine appropriate treatment measures and establish clear responsibilities. This enables organizations to prioritize investments, strengthen accountability and make informed decisions about information security.
Information Security Governance and ISO 27001
A well-functioning Information Security Management System (ISMS) provides the foundation for structured and continuous risk management.
We support organizations with the implementation and improvement of ISO 27001, including risk assessments, policies, control frameworks, internal audits, management reviews and continuous improvement.
Our focus is on integrating information security into existing business processes, rather than creating unnecessary administrative complexity.
NIS2 and DORA Compliance
Regulatory requirements increasingly emphasize operational resilience, management accountability and effective ICT risk management.
We help organizations assess their readiness for NIS2 and DORA, identify gaps and implement practical measures covering incident management, business continuity, third-party risk management and security governance.
Our approach takes into account the organization's specific regulatory obligations and operational context.
From Compliance to Effective Control
Compliance is not simply about having policies and procedures in place. Organizations must also understand whether their controls operate effectively.
We help evaluate control design, assess implementation, identify weaknesses and establish monitoring and reporting processes.
By connecting risk management, governance and operational controls, we help organizations move beyond checklist compliance towards sustainable information security.
Independent Expertise, Practical Results
Contrisity combines specialist knowledge of information security, risk management and assurance with a pragmatic approach.
Whether your organization is implementing ISO 27001, preparing for NIS2 or DORA, or improving its existing security governance, we provide clear guidance and hands-on support tailored to your needs.
Strengthen your information security with a practical, risk-based approach that supports both compliance and business resilience.
Why It Matters
As organizations become increasingly digital and interconnected, information security risks have a direct impact on business continuity, regulatory compliance and stakeholder trust.
Frameworks such as ISO 27001, NIS2 and DORA require organizations to demonstrate that risks are identified, assessed and managed through effective governance and controls.
A structured, risk-based approach helps organizations protect critical information, strengthen operational resilience and make informed decisions without creating unnecessary complexity.
Aditional Benefits
Better Risk Visibility
Gain a clear understanding of information security risks, priorities and responsibilities, enabling management to make informed decisions.
Stronger Regulatory Compliance
Align your security governance and controls with relevant requirements under ISO 27001, NIS2 and DORA.
Improved Operational Resilience
Reduce vulnerabilities, strengthen incident preparedness and improve your organization's ability to respond to disruptions.
Practical and Proportionate Controls
Implement security measures that reflect your organization's actual risks, size and complexity, rather than introducing unnecessary bureaucracy.
Sustainable Continuous Improvement
Establish a structured approach to monitoring, evaluating and improving information security over time.
