
Audit & Assurance
Contrisity provides independent external audit and assurance services through its audit partners, alongside internal audit and advisory services. We maintain a clear separation between these activities to safeguard auditor independence.
What We Offer
External Audit & Assurance
Through our audit partners, we perform independent assurance engagements that help organizations demonstrate the effectiveness of their internal controls to customers, regulators and other stakeholders.
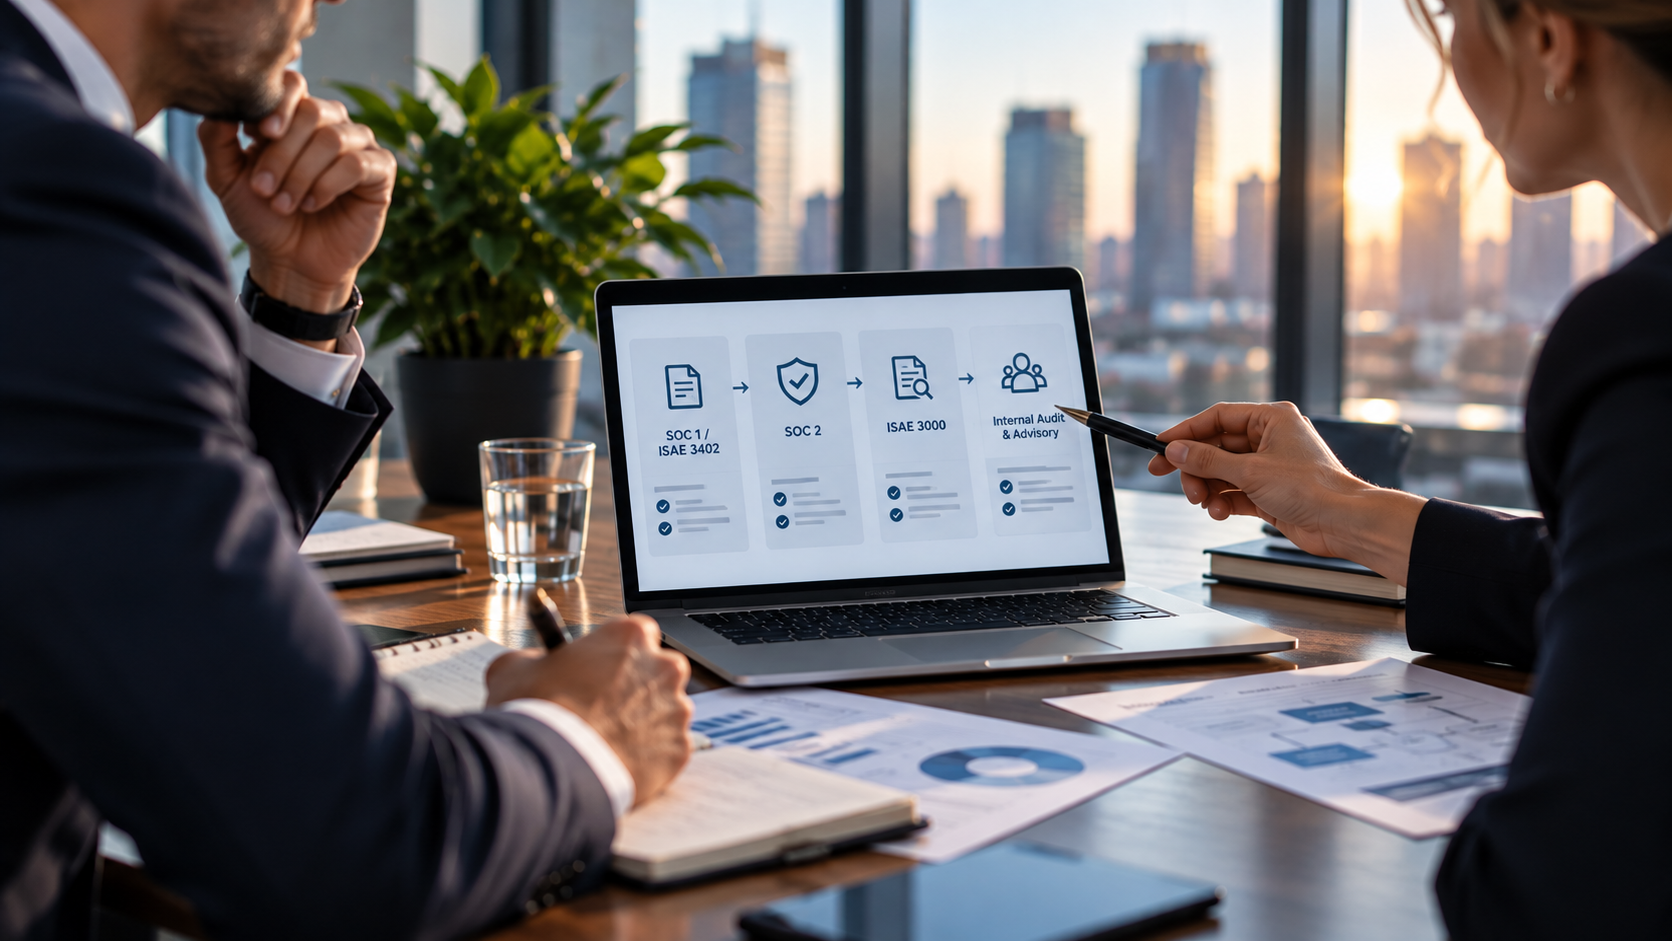
SOC 1 / ISAE 3402
We perform assurance engagements focused on controls relevant to customers' financial reporting. These engagements assess the design and, for Type 2 reports, the operating effectiveness of controls at service organizations.
SOC 2 Assurance
We perform SOC 2 engagements covering relevant Trust Services Criteria, including security, availability, processing integrity, confidentiality and privacy. Our approach focuses on meaningful controls, appropriate evidence and clear reporting.
ISAE 3000 & Specialized Assurance
We support independent assurance engagements covering specific control frameworks, regulatory requirements and non-financial subject matters, tailored to the intended users and applicable assurance criteria.
Internal Audit & Advisory
We provide internal audits, control assessments, audit readiness support and practical advice to strengthen governance, risk management and internal control environments.
Independence is fundamental to our approach. We do not combine advisory or internal audit activities with external assurance engagements where this would compromise auditor independence.
Audit & Assurance
Audit & Assurance
Reliable internal controls are essential for organizations that want to demonstrate accountability, manage risks and build trust with customers, regulators and other stakeholders.
At Contrisity, we combine extensive experience in IT auditing, internal control and assurance with a practical, risk-based approach. We provide independent external audit and assurance services through our audit partners, as well as internal audit and advisory services.
Our services are structured to safeguard auditor independence. We do not combine advisory or internal audit responsibilities with external assurance engagements where this would create a conflict of interest.
Independent External Audit & Assurance
Organizations increasingly rely on independent assurance to demonstrate that their internal controls are appropriately designed and operating effectively.
Through our audit partners, we perform external assurance engagements based on internationally recognized standards and established audit methodologies.
Our approach emphasizes relevant risks, meaningful testing, reliable evidence and transparent reporting.
SOC 1 & ISAE 3402
SOC 1 and ISAE 3402 reports provide assurance over controls at service organizations that are relevant to their customers' financial reporting.
We perform both Type 1 and Type 2 engagements, depending on the reporting objectives and requirements of the intended users.
Our work includes understanding the service organization's control environment, assessing relevant risks, evaluating control design and, for Type 2 engagements, testing operating effectiveness over a defined period.
SOC 2 Assurance
SOC 2 reporting enables service organizations to demonstrate how their controls address relevant Trust Services Criteria.
These criteria cover security, availability, processing integrity, confidentiality and privacy.
We perform SOC 2 engagements tailored to the organization's services, systems, commitments and applicable criteria. Our audits focus on effective controls and appropriate evidence rather than unnecessary documentation.
ISAE 3000 & Specialized Assurance
Not all assurance requirements fit within SOC 1 or SOC 2 reporting.
Through our audit partners, we also perform specialized assurance engagements under ISAE 3000 and other applicable standards, addressing specific control frameworks, regulatory requirements or non-financial subject matters.
The scope, criteria and reporting approach are determined based on the engagement objectives and intended users.
Internal Audit & Advisory
In addition to external assurance, Contrisity supports organizations in strengthening their internal control environment.
Our services include internal audits, control assessments, audit readiness reviews, risk assessments and advisory support relating to governance, information security and compliance.
We help organizations identify control weaknesses, prioritize improvements and establish sustainable processes that support effective risk management.
These services are provided separately from external assurance engagements where independence requirements prevent combining the two roles.
A Practical, Risk-Based Audit Approach
We believe effective auditing starts with understanding the organization, its services and its most significant risks.
Rather than focusing solely on checklists, we assess whether controls address relevant risks and whether sufficient evidence exists to demonstrate their effectiveness.
This approach supports efficient audit execution, clear communication and reporting that provides meaningful value to stakeholders.
Independence, Expertise and Trust
Auditor independence is fundamental to credible assurance.
Contrisity maintains a clear distinction between independent external assurance and internal audit or advisory activities. Engagement acceptance, responsibilities and potential conflicts of interest are assessed to safeguard the integrity of our work.
With experience across complex IT environments, outsourced services and regulatory frameworks, we help organizations achieve reliable assurance and stronger internal control.
Whether you require independent external assurance or support in improving your internal controls, Contrisity provides specialist expertise tailored to your organization's needs.
Why It Matters
Organizations are increasingly expected to demonstrate that their internal controls are not only properly designed, but also operate effectively. Customers, regulators and other stakeholders require reliable assurance over critical processes, information systems and outsourced services.
Independent external assurance, including SOC 1, SOC 2 and ISAE engagements, helps organizations build trust and demonstrate the effectiveness of their control environment. Internal audits and advisory services provide valuable insights into risks, control weaknesses and opportunities for improvement.
At Contrisity, we offer both external audit and assurance services through our audit partners, and internal audit and advisory services. These activities are kept separate where required to safeguard independence and avoid conflicts of interest.

Aditional Benefits
Greater Stakeholder Confidence
Build trust with customers, regulators and business partners through transparent reporting and, where applicable, independent assurance over internal controls.
Stronger Internal Controls
Gain insight into control design and operating effectiveness, helping your organization identify weaknesses and improve its control environment.
Reduced Audit Complexity
Benefit from a structured, risk-based audit approach that focuses on relevant risks, meaningful evidence and efficient execution.
Clear and Actionable Insights
Receive practical findings and recommendations that support better decision-making, stronger governance and continuous improvement.
Access to Specialized Expertise
Work with experienced IT audit and assurance professionals who understand complex IT environments, regulatory requirements and internationally recognized assurance standards.
